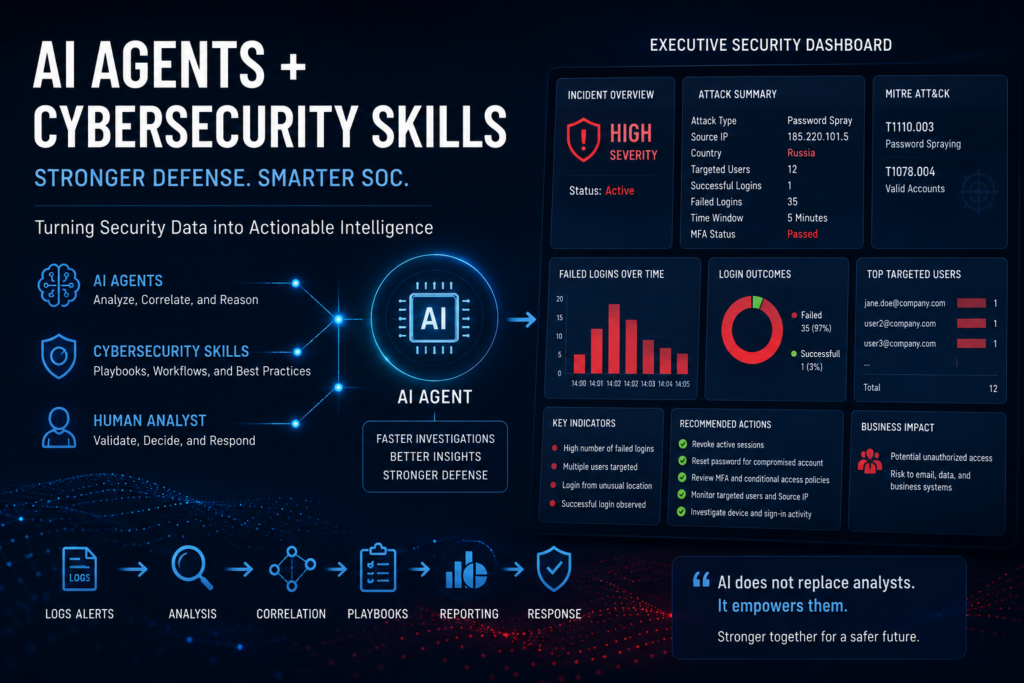
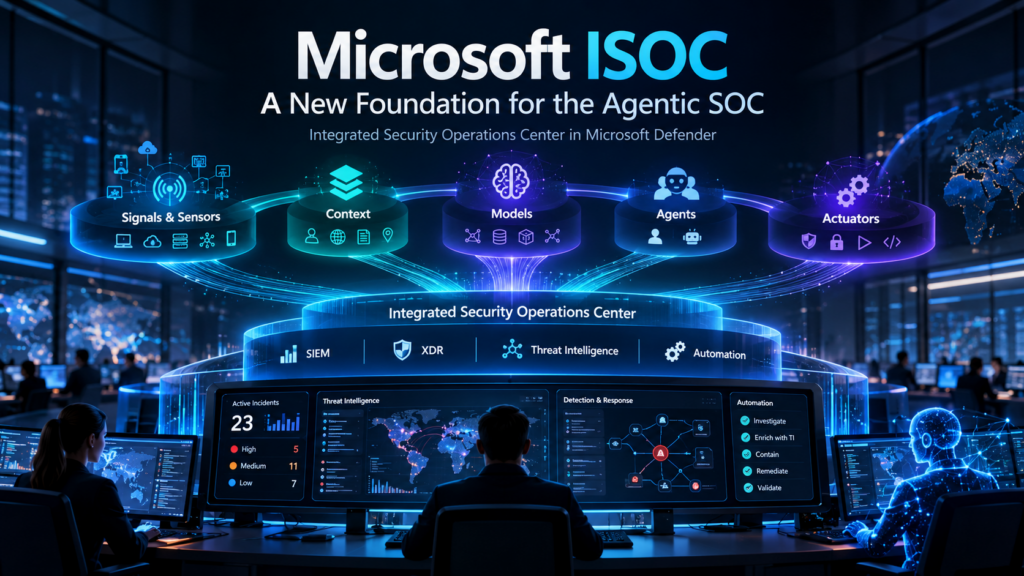
Last week, Microsoft announced Integrated Security Operations Center (ISOC) in Microsoft Defender, a new approach to security operations designed for the agentic AI era.
The announcement caught my attention because Microsoft is not simply adding another AI assistant to the SOC.
The bigger idea is to bring SIEM, XDR, threat intelligence, automation, security context, and AI agents into one integrated security operations foundation.
So, what exactly is Microsoft ISOC?
ISOC stands for Integrated Security Operations Center.
It is not a new standalone Microsoft product.
Instead, Microsoft is bringing security operations capabilities together inside the Microsoft Defender experience, including:
- Microsoft Sentinel SIEM capabilities
- Microsoft Defender XDR
- Threat intelligence
- Automation
- AI and security agents
- First-party and third-party security data
The goal is to give both security analysts and AI agents access to the same signals, context, and controls so they can detect, investigate, and respond from a shared platform.
Microsoft describes the model very simply:
See → Understand → Act
For me, that is the key idea behind ISOC.
Why does this matter?
Most enterprise SOCs today are built from multiple security technologies.
You may have:
EDR + SIEM + Email Security + Identity Security + Cloud Security + Threat Intelligence + SOAR
Each product provides useful capabilities, but security teams often spend significant time connecting these platforms, moving between consoles, rebuilding context, and maintaining integrations.
That becomes even more challenging when AI agents are introduced.
An AI security agent needs more than access to an LLM.
It needs access to:
Signals
What is happening across endpoints, identities, email, cloud, network, and applications?
Context
Is this device critical?
Is the user privileged?
Is this IP malicious?
Is there an active attack path?
Controls
Can the system actually take defensive action?
For example:
- Isolate an endpoint
- Revoke a user session
- Remove a malicious email
- Block an indicator
- Trigger an investigation or response workflow
This is where Microsoft ISOC becomes interesting.
Microsoft is trying to make these capabilities part of one security operations architecture rather than something organizations have to assemble themselves.
Built for Humans and AI Agents
Microsoft describes ISOC as a foundation for agentic security.
The concept is that humans and AI agents operate together using the same security environment.
Microsoft summarizes this direction with:
“Strategy stays human. Scale becomes autonomous.”
In practical terms, AI agents could increasingly help security teams with repetitive SOC activities such as:
- Alert triage
- Incident investigation
- Threat enrichment
- Timeline creation
- Correlating activity across identities, endpoints, and cloud resources
- Recommending remediation
- Executing approved response actions
Meanwhile, analysts remain responsible for priorities, judgment, security strategy, and high-impact decisions.
This could gradually change the role of SOC analysts from manually executing every investigation step toward supervising and directing autonomous security operations.
What Happens to Microsoft Sentinel?
One important point: Microsoft Sentinel is not disappearing.
Instead, Microsoft continues integrating Sentinel capabilities into the Defender experience.
ISOC takes that integration further by combining SIEM and XDR capabilities inside a unified security operations platform.
So instead of thinking about:
Microsoft Sentinel + Defender XDR + Automation + AI
as separate components, Microsoft’s direction is increasingly:
Microsoft Defender as the integrated security operations platform.
Why I Think This Announcement Is Important
For me, the most important part of ISOC is not the product name.
It is the architectural direction Microsoft is taking.
Security operations are moving from:
Security tools generating alerts → Humans investigating everything manually
Security platforms providing signals, context, and controls → Humans and AI agents operating together
That is a fundamental change.
The next-generation SOC will probably not be defined by how many AI features it has.
The important question will be:
Can people and AI agents securely perceive, reason, and act across the environment using the same context and controls?
That is exactly the problem Microsoft is trying to address with ISOC.
Microsoft ISOC in Defender is currently available in preview.